The internet has created countless legitimate digital marketplaces, but it has also enabled underground ecosystems where stolen information, compromised accounts, and other illicit digital assets may be discussed or traded. bclub is a name that has appeared in online discussions associated with underground payment-card activity, while bclub.tk has been referenced in connection with that name.
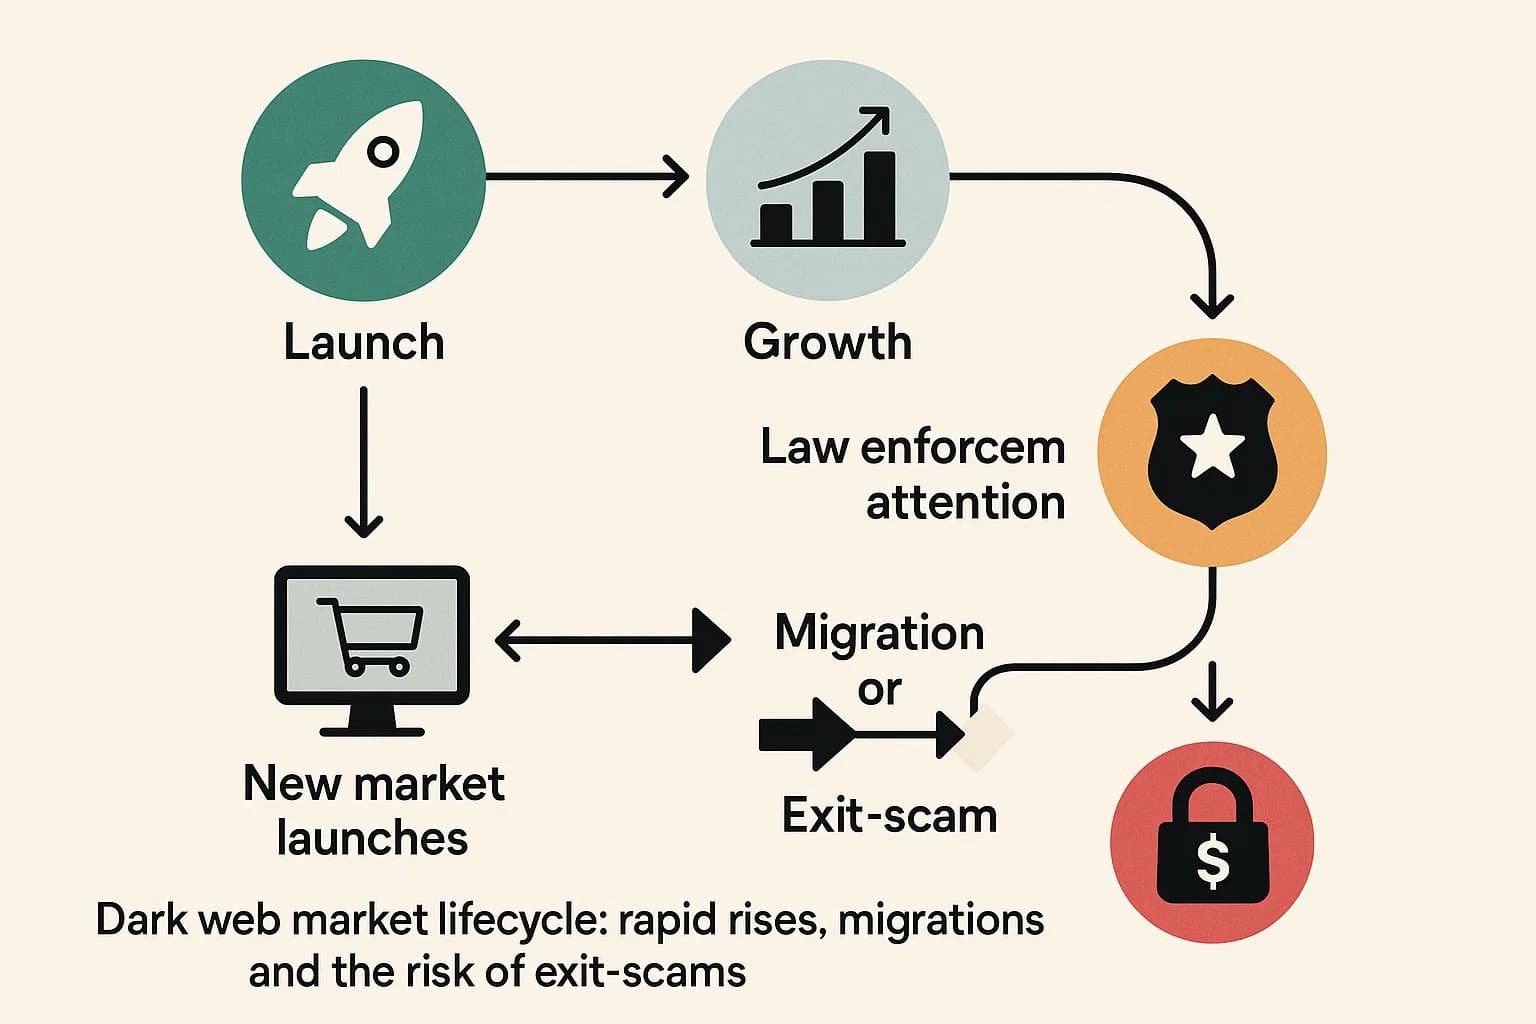
However, it is important to separate online claims from independently verified information. The ownership, history, current operation, and exact activities associated with a particular BClub or bclub.tk domain may be difficult to establish reliably. Underground services can disappear, change domains, be impersonated, or become the subject of misleading advertisements and forum posts.
This article examines the rise, reputation, and risks associated with BClub and bclub.tk from a cybersecurity perspective.
What Is BClub?
BClub is generally discussed in the context of underground online marketplaces and communities involving compromised payment information. These environments are sometimes associated with carding, a term used to describe fraudulent activity involving stolen payment-card information.
The information discussed in such environments can include payment-card details obtained through criminal means. The broader ecosystem may also involve compromised accounts, stolen credentials, personal information, and other forms of illegally obtained data.
Because underground communities deliberately operate outside normal regulatory and legal frameworks, publicly available information about individual platforms can be incomplete or contradictory. A website name alone is therefore not enough to establish who operates it or what is currently happening on the service.
For researchers and internet users, this distinction matters. Treating an online claim as a verified fact can create unnecessary security risks and spread inaccurate information.
The Role of bclub.tk in Online Discussions
The domain bclub.tk has been associated in some online discussions with the BClub name. Domain-based identities can be particularly difficult to verify in underground environments.
A domain can change ownership, stop resolving, redirect somewhere else, or be copied by an unrelated party. Screenshots and forum advertisements can also be outdated or manipulated.
For that reason, claims about bclub.tk should be evaluated carefully. Questions worth asking include:
- Who independently verified the service?
- Is the information supported by reputable cybersecurity research?
- Is the domain currently active or merely referenced in older material?
- Could the site be an impersonation or phishing operation?
- Are claims based on evidence or anonymous posts?
These questions are useful because criminals can become victims of scams themselves. An underground site promising illicit services does not necessarily provide what its operators claim.
Why Stolen Card Data Is Valuable to Criminals
Payment-card information can have significant value to criminals because compromised financial information may be used as part of fraudulent transactions or broader identity-related schemes.
Card information can be exposed through several common attack methods, including:
Data Breaches
Cybercriminals may steal information from organizations that experience security breaches. Retailers, online services, financial organizations, and other businesses can become targets.
A breach does not necessarily mean that a company intentionally exposed customer information. Attackers may exploit vulnerabilities, compromised credentials, insecure systems, or weaknesses in third-party services.
Phishing
Phishing campaigns attempt to trick people into revealing sensitive information. Fake login pages, fraudulent emails, deceptive messages, and impersonated organizations are common examples.
Malware
Malicious software can compromise devices and potentially capture sensitive information. Keeping operating systems, browsers, and security software updated is therefore an important part of digital security.
Social Engineering
Attackers can manipulate people into revealing information or approving actions that they would normally reject. Social engineering demonstrates why cybersecurity is not only a technical problem—it is also a human one.
Reputation in Underground Communities
The concept of reputation is unusual in criminal online marketplaces. Participants may discuss whether a particular service is reliable, but these claims should not be confused with the reputation systems used by legitimate businesses.
Anonymous users can create multiple identities, make exaggerated claims, or deliberately spread misinformation. Competitors may also attempt to damage another service’s reputation.
This creates a major problem for anyone researching BClub-related claims. A collection of forum posts does not automatically constitute reliable evidence.
A more responsible approach is to compare claims against information from established cybersecurity researchers, law-enforcement announcements, security companies, and reputable investigative reporting.
Security Risks Associated With Underground Websites
People sometimes focus only on the illegal nature of underground marketplaces and overlook another major issue: visiting unfamiliar criminal-oriented websites can create cybersecurity risks of its own.
Potential dangers include:
- Phishing pages designed to steal passwords
- Malicious downloads
- Browser or device exploitation
- Fake login forms
- Credential harvesting
- Financial scams
- Tracking and privacy exposure
- Impersonation websites
- Attempts to collect personal information
A person searching for information about an underground service can therefore encounter secondary scams that have nothing to do with the original platform.
This is particularly important when a domain has an uncertain history. Even if an address was once associated with a particular service, that does not prove that a later version of the website is legitimate or controlled by the same operators.
The Broader Impact of Carding
The consequences of stolen payment information extend far beyond individual unauthorized transactions.
Consumers can experience financial disruption, account problems, replacement-card requirements, and privacy concerns. Businesses can face chargebacks, investigation costs, customer-support expenses, reputational damage, and additional security requirements.
Financial institutions also invest significant resources in fraud detection and prevention. As attackers develop new techniques, banks and payment companies continually improve monitoring systems, authentication mechanisms, and transaction-risk analysis.
Ultimately, the victims of payment-card theft are often ordinary consumers and businesses that had no connection to the criminal activity.
How Consumers Can Protect Their Payment Information
Understanding the risks associated with BClub, bclub.tk, and similar underground ecosystems is less useful without practical defensive measures.
Consumers can reduce exposure by:
- Enabling transaction alerts. Notifications can make suspicious activity easier to identify quickly.
- Using strong, unique passwords. Reusing passwords increases the impact of a compromised account.
- Activating multi-factor authentication. MFA provides an additional layer of protection for supported accounts.
- Keeping devices updated. Security patches can address vulnerabilities that attackers might otherwise exploit.
- Being cautious with unexpected messages. Avoid entering financial information through links received in suspicious emails or messages.
- Protecting authentication codes. Legitimate organizations generally do not need customers to disclose one-time verification codes to strangers.
- Reviewing financial statements regularly. Unfamiliar transactions should be investigated promptly through the relevant financial institution.
What Businesses Can Learn From Carding Threats
Businesses have an important role in reducing the supply of stolen payment information.
Security programs should include access controls, strong authentication, vulnerability management, network monitoring, secure payment processing, employee awareness training, and incident-response planning.
Organizations should also evaluate third-party vendors because attackers sometimes target suppliers or service providers as an indirect route into larger businesses.
Payment security is particularly important because a compromise can affect both the organization and its customers.
Separating Facts From Online Claims
One of the most important lessons from discussions surrounding BClub and bclub.tk is the need for source verification.
Search results, anonymous forum posts, screenshots, social-media claims, and promotional messages can provide clues, but they should not automatically be treated as authoritative evidence.
A responsible cybersecurity researcher should look for corroboration from multiple independent sources and pay attention to publication dates. Historical references should also be clearly separated from information about current activity.
This approach prevents researchers from accidentally amplifying misinformation or outdated claims.
The Role of Law Enforcement and Cybersecurity Researchers
Payment-card fraud is an international problem, meaning investigations can involve financial institutions, cybersecurity companies, national law-enforcement agencies, and international partners.
Authorities may investigate infrastructure, identify criminal networks, seize domains or servers, and pursue individuals involved in cybercrime. Security researchers can contribute by identifying malicious infrastructure, studying attack patterns, and helping organizations understand emerging threats.
These efforts demonstrate why underground marketplaces should be viewed as part of a broader cybersecurity problem rather than simply as isolated websites.
The Future of Payment Security
Payment security continues to evolve as financial technology changes. Tokenization, stronger authentication, real-time fraud monitoring, behavioral analysis, and improved transaction-risk systems can make stolen payment information harder to abuse.
At the same time, criminals continue looking for weaknesses in people, organizations, and digital systems. This means cybersecurity will remain an ongoing process rather than a one-time solution.
For consumers, the most valuable lesson is simple: protecting financial information requires both technical safeguards and careful online behavior.
Conclusion
BClub and bclub.tk have appeared in online discussions concerning underground payment-card activity, but claims about their exact history, operators, reputation, or current status should be treated cautiously unless supported by reliable independent evidence.
The broader issue is more clearly established: stolen payment-card information creates serious financial, privacy, and cybersecurity risks. Criminal marketplaces can contribute to this ecosystem, while their users may also face scams, phishing, malware, and exposure to other threats.
Understanding these risks helps consumers, businesses, and cybersecurity researchers focus on what matters most—protecting sensitive information, detecting fraud early, verifying online claims, and strengthening the systems that criminals attempt to exploit.
Rather than viewing BClub or bclub.tk simply as an isolated website, it is more useful to understand the subject as part of the wider challenge of payment-card theft and online financial crime. Strong security practices, reliable threat intelligence, and informed digital behavior remain essential tools for reducing that risk.